Improving Algorithmic Efficiency Using Cryptography
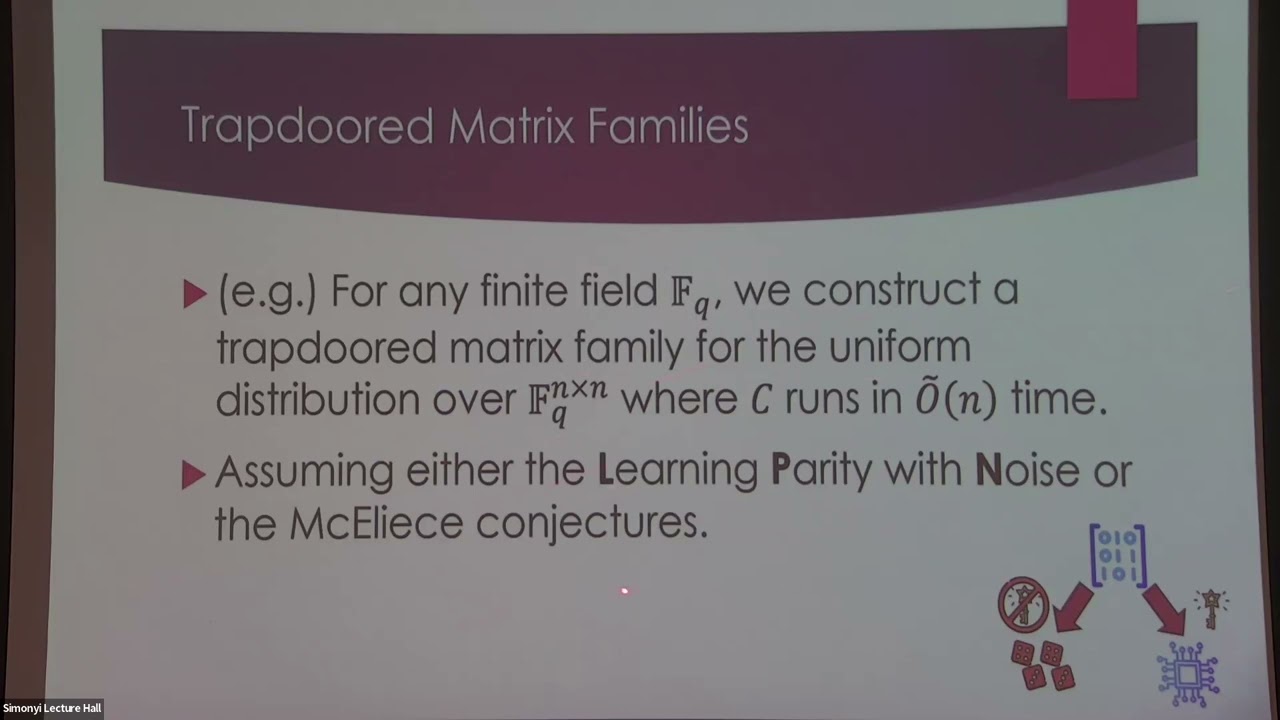
Or Zamir of Tel Aviv University presents this Institute for Advanced Study Computer Science and Discrete Mathematics seminar on using cryptographic tools to speed up ordinary algorithms. His claim is that under standard cryptographic hardness assumptions, certain computational problems admit algorithms that are asymptotically faster than the best known unconditional ones, while still always returning correct answers. Zamir introduces a new tool he calls Trapdoor Matrix Distributions, and uses it to build the first worst-case to average-case reduction for matrix multiplication with optimal parameters, improving on a 2025 result, along with similar reductions for matrix inversion and other linear algebra operations. He also describes faster general-purpose dimension reduction techniques and a method for speeding up inference time in classification models. The work is joint with Vinod Vaikuntanathan. The talk is aimed at a technical audience already comfortable with complexity theory and cryptographic assumptions, walking through the constructions and their implications step by step.